
Fashion ID: When a Facebook “Like” Button Makes a Website a Joint Controller
One little “Like” button. Shared responsibility for visitors’ data. In Fashion ID, the CJEU explains how a website can become a joint controller before anyone clicks—and why responsibility depends on which processing operations it helps determine.
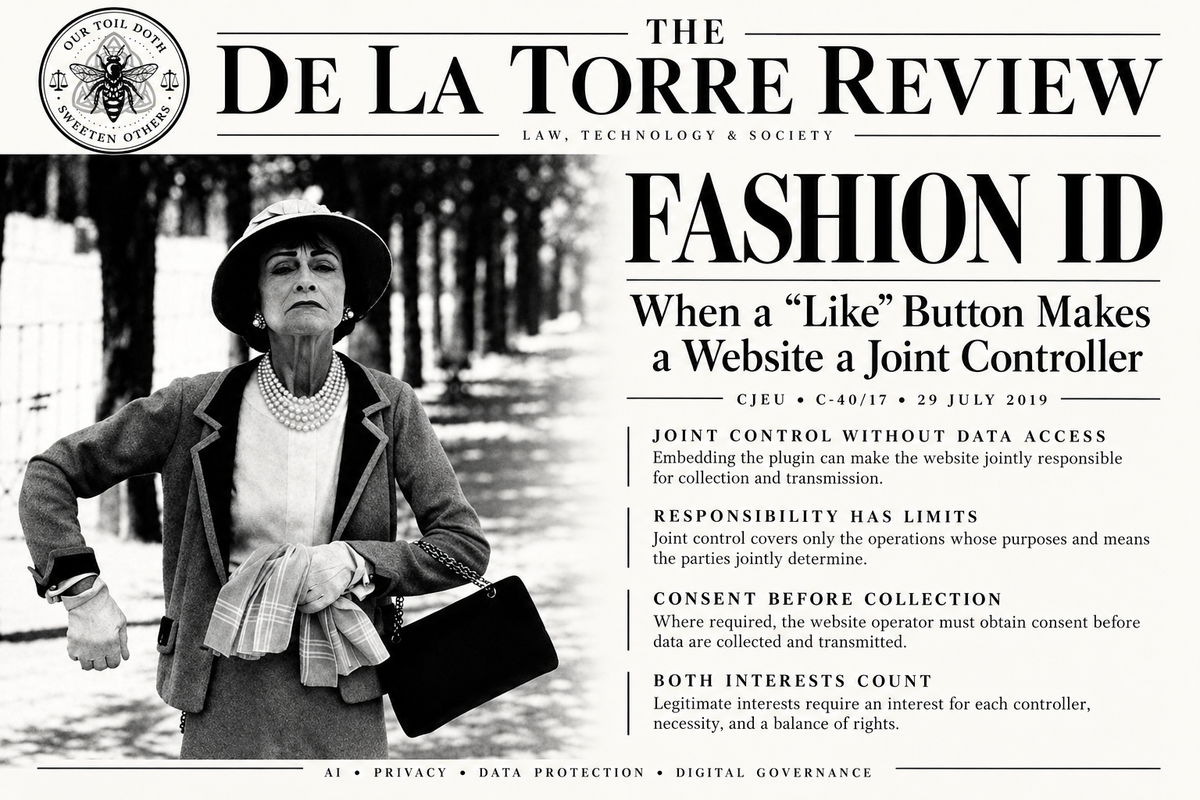
Case C-40/17 | Fashion ID GmbH & Co. KG v Verbraucherzentrale NRW eV | Court of Justice of the European Union | Second Chamber | 29 July 2019
Practice Takeaways: ① Embedding a plugin can create joint controllership. Choosing a tool that collects and transmits visitors’ personal data for complementary commercial purposes can involve jointly determining the processing. ② Access to the data is not required. An operator can be a joint controller even if the data travel directly from the visitor’s browser to the platform. ③ Identify the relevant operations. Joint control over collection and transmission does not automatically extend to the recipient’s subsequent processing. ④ Consent must come before the processing it authorizes. Where consent is required, the website operator cannot leave it to a platform that receives the data after transmission has occurred. ⑤ Legitimate interests require more than a commercial benefit. Each joint controller must pursue a legitimate interest, and necessity and the balancing of rights remain essential. ⑥ Non-members have data-protection rights too. Visiting a website can expose someone’s data to a social network they have never joined.
A visitor opens an online clothing store. Before clicking anything—and whether or not they have a Facebook account—their browser sends personal data to Facebook because the retailer has embedded a “Like” button.
Who is responsible for that transfer?
In Fashion ID, the Court held that the retailer could be a controller jointly with Facebook for collecting and transmitting those data. The retailer’s decision to embed the button, together with the commercial purposes served by that arrangement, mattered even though the retailer did not itself receive the information. (Judgment, paras. 75–85.)
But the Court also defined a boundary. Joint controllership must be assessed for the particular operation or set of operations whose purposes and means the parties jointly determine. It does not automatically follow the data through everything the recipient later does with them. (Judgment, paras. 70–76.)
Practice Tip: Review what an integration causes to happen when a page loads. A feature presented as a social button may already be collecting and transmitting personal data before the visitor chooses to use it.
What happened
Fashion ID, an online clothing retailer, embedded Facebook’s “Like” social plugin on its website. To display third-party content of this kind, a visitor’s browser requests content from the third-party provider and transmits information needed for that exchange, including the computer’s IP address and technical information about the browser. (Judgment, paras. 25–26.)
According to the referring court’s account, the plugin caused visitors’ personal data to be transmitted to Facebook Ireland as soon as they consulted Fashion ID’s website. The transmission appeared to occur without visitors being aware of it, regardless of whether they had clicked the button or were members of Facebook. (Judgment, para. 27.)
Verbraucherzentrale NRW, a German consumer-protection association, sought an injunction. It alleged that Fashion ID transmitted visitors’ data without consent and failed to provide the required information. The Regional Court in Düsseldorf partly upheld its claims. Fashion ID appealed, and Facebook Ireland intervened in its support. (Judgment, paras. 28–31.)
Fashion ID disputed both the association’s standing and its own status as a controller. It argued that it had no influence over the data transmitted by the visitor’s browser or Facebook’s subsequent use of those data. (Judgment, paras. 32–34.)
The Higher Regional Court in Düsseldorf referred questions to the CJEU concerning consumer-association litigation, controllership, legitimate interests, consent, and transparency.
NOTE: The case arose under Directive 95/46, the predecessor to the GDPR. The Court’s reasoning on joint controllership has since been expressly incorporated into EDPB guidance under the GDPR.
Why the case matters
Fashion ID addresses a familiar problem in online services: an organization chooses a third-party tool, but the resulting personal data flow directly to the tool’s provider.
Looking only at who holds the data would miss the organization’s role in causing the collection and transmission. Fashion ID makes clear that an entity can influence processing for its own purposes without operating the recipient’s servers or receiving the resulting records. (Judgment, paras. 68–69, 77–82.)
At the same time, the judgment avoids treating a commercial relationship as a single, undifferentiated processing activity. Collection, disclosure, storage, and later use are distinct operations. An organization’s role must be examined in relation to the operations it actually helps determine. (Judgment, paras. 70–76.)
When reviewing embedded content and other integrations: examine both the decision that enables the transfer and the limits of the organization’s participation in what happens afterward.
Key holding
The operator of a website that embeds a social plugin causing visitors’ browsers to transmit personal data to the plugin provider can be a controller jointly with that provider for the collection and disclosure by transmission. The operator’s lack of access to the data does not prevent that conclusion. (Judgment, paras. 69, 82, 85.)
Its status as a controller is limited to the operations whose purposes and means it jointly determines. On the facts described, Fashion ID could not be treated as a controller for Facebook’s subsequent processing over which it did not exercise that influence. The factual assessment remained subject to verification by the national court. (Judgment, paras. 74–85.)
For the jointly controlled operations, the website operator also has transparency obligations and must obtain the consent contemplated by the Directive before collection and transmission. If processing is instead assessed under the legitimate-interests provision, both the operator and provider must each pursue a legitimate interest, subject to the provision’s other requirements. (Judgment, paras. 93–106.)
The Court’s analysis
1. Controllership depends on influence over purposes and means
The Directive defined a controller as an entity that, alone or jointly with others, determines the purposes and means of processing personal data. The Court interpreted that definition broadly to ensure effective and complete protection of individuals. More than one entity can participate as a controller in the same processing. (Judgment, paras. 65–67.)
An entity that influences processing for its own purposes and thereby participates in determining its purposes and means may qualify. Neither exclusive control nor access to the personal data is necessary. (Judgment, paras. 68–69.)
For Fashion ID, the relevant influence came from embedding the plugin. The Court considered that the retailer appeared to have installed it while aware that it collected and transmitted visitors’ data. That choice exerted a decisive influence over collection and transmission: those operations would not have occurred in that way without the plugin. (Judgment, paras. 75, 77–79.)
The commercial purposes also mattered. The button allowed Fashion ID to increase the visibility of its goods on Facebook. Facebook, in turn, obtained data for its own commercial purposes. Subject to the national court’s investigations, the Court considered that this arrangement supported joint determination of the purposes of collection and transmission. (Judgment, paras. 80–81.)
The fact that Facebook supplied the technology did not resolve who controlled the resulting processing.
Practice Tip: When assessing an integration, document why the organization uses it, what data flows it enables, and what purposes the provider pursues. The fact that a provider designed and hosts the tool does not, by itself, establish a processor relationship.
2. Joint control has to be assessed operation by operation
The Court then explained the limiting principle.
Processing can consist of one operation or a series of operations. The Directive’s definition included collection, storage, consultation, use, disclosure by transmission, and erasure. Participation in one stage does not necessarily establish participation in every other stage. (Judgment, paras. 71–74.)
For Fashion ID, the relevant jointly determined operations were collection and disclosure by transmission. On the information before the Court, the retailer did not determine the purposes and means of Facebook’s subsequent processing after transmission. It therefore could not be considered a controller for those subsequent operations on that basis. (Judgment, para. 76.)
Entities may participate in the processing at different stages and to different degrees; their respective responsibility must be assessed in light of all relevant circumstances. (Judgment, para. 70.)
Joint responsibility does not necessarily mean equal responsibility.
Practice Tip: Map the processing before assigning roles. Distinguish collection and transmission from later matching, profiling, advertising, retention, and deletion, and examine which decisions each party makes at each stage. The endpoint of joint control depends on the facts of the arrangement.
3. Lack of access does not remove responsibility
Fashion ID did not need to receive the personal data transmitted to Facebook to qualify as a joint controller for that transmission. The Court expressly rejected access to the data as a necessary condition. (Judgment, para. 82.)
That matters whenever information travels directly from a browser or device to a third party. The technical route may bypass the website operator’s systems while still resulting from the operator’s decision to deploy the tool for its own purposes.
The Court also emphasized the position of visitors without Facebook accounts. For those individuals, simply viewing a website with the button appeared to trigger processing by a social network they had not joined. The Court considered that the website operator’s responsibility appeared even greater in that situation. (Judgment, para. 83.)
4. Both controllers’ legitimate interests matter
The referring court asked whose interests should be considered under Article 7(f) of the Directive: Fashion ID’s or Facebook’s.
The Court answered that each joint controller must pursue a legitimate interest through the relevant collection and transmission for those operations to be justified in respect of each of them. (Judgment, paras. 96–97.)
It also restated the three cumulative conditions for relying on legitimate interests: a legitimate interest must be pursued; the processing must be necessary for that interest; and the individual’s protected interests or fundamental rights and freedoms must not take precedence. (Judgment, paras. 94–95.)
The Court did not determine that the plugin satisfied those conditions. A commercial advantage helped explain why the parties participated in the processing; it did not establish that the processing was lawful.
Practice Tip: Separate the role analysis from the lawful-basis analysis. Evidence that both parties benefit from processing may help explain joint control, but it does not establish necessity or resolve the balancing of interests and rights.
5. Consent must be obtained before collection and transmission
The Court placed the duty to obtain the consent referred to in Articles 2(h) and 7(a) on the website operator for the operations it jointly controlled. That consent had to precede collection and transmission. (Judgment, paras. 100–102, 106.)
The timing followed the design of the integration. Visiting Fashion ID’s website triggered the processing. Leaving consent solely to Facebook, which became involved later, would fail to provide efficient and timely protection. (Judgment, para. 102.)
The scope of that duty followed the same boundary as controllership: the consent to be obtained by Fashion ID concerned the operations whose purposes and means it actually determined. The Court did not impose on Fashion ID a consent duty for every separate processing operation Facebook might subsequently undertake. (Judgment, paras. 101–102.)
6. ePrivacy creates a separate question
The Commission argued that the legitimate-interests question was irrelevant because consent was required under Article 5(3) of the ePrivacy Directive for access to information stored on a visitor’s device. (Judgment, para. 88.)
The Court left it to the national court to investigate whether Facebook accessed stored information in the circumstances of the case. It proceeded to address legitimate interests because the personal data being transmitted were not necessarily confined to information stored on the device. (Judgment, paras. 89–92.)
The distinction is practical. A lawful-basis assessment for personal-data processing and an assessment of the rules governing storage of, or access to, information on a device address different questions.
A legitimate interest does not itself dispense with an applicable ePrivacy consent requirement.
Practice Tip: Review device access and personal-data processing separately. Where prior consent is required, verify that the technical implementation prevents the relevant collection and transmission until that consent has been obtained. A notice displayed after the transfer cannot supply prior consent.
7. The website operator must provide information at collection
The Court likewise held that Fashion ID had its own duty to inform visitors under Article 10 of the Directive. The information had to be provided when the data were collected. Its scope concerned the operations whose purposes and means the retailer actually determined. (Judgment, paras. 103–106.)
8. Consumer associations could bring proceedings under national law
Fashion ID also challenged the consumer association’s standing, arguing that the Directive reserved remedies to affected individuals and supervisory authorities.
- The Court rejected that interpretation. Articles 22–24 did not exhaustively harmonize national judicial remedies and did not preclude legislation allowing consumer-protection associations to bring proceedings against an alleged infringer. Such proceedings could support implementation of the Directive without undermining supervisory authorities’ independence. (Judgment, paras. 43–63.)
- The Court referred to Article 80(2) GDPR as confirmation of the legislature’s approach, while deciding the question under the earlier Directive. It did not create an unrestricted EU-wide right for any association to sue under any circumstances. (Judgment, paras. 62–63.)
The Advocate General’s Opinion
Advocate General Michal Bobek’s Opinion provides the conceptual explanation for the judgment’s boundaries.
- He questioned whether an increasingly expansive understanding of joint control would improve protection if it imposed obligations on entities that lacked the knowledge or practical ability to fulfill them. Responsibility needed a reasonable connection to the influence actually exercised over processing. (Opinion, paras. 71–93.)
- His proposed solution was to read the definitions of “processing” and “controller” together. Processing consists of identifiable operations. Joint controllers should be responsible for the operations whose purposes and means they co-determine, rather than an undefined collection of everything that happens to the data. (Opinion, paras. 97–101.)
- Applied to Fashion ID, both parties appeared to have voluntarily enabled collection and transmission through the plugin for complementary commercial purposes. The retailer’s responsibility should extend to those operations, without spilling into subsequent processing outside its control. (Opinion, paras. 102–108.)
- Bobek also explained why the retailer had to obtain consent: its website triggered the processing, so consent given only to a party involved afterward would come too late. (Opinion, paras. 131–134.)
The Court substantially followed this approach. Its express reliance on paragraph 101 of the Opinion when defining the limits of joint controllership makes the relationship particularly clear. (Judgment, para. 74.)
From the WP29 opinion to EDPB guidance
The earlier opinion provides context
The Article 29 Working Party’s Opinion 5/2009 on online social networking predates Fashion ID by a decade. It identified social-network providers as controllers and recognized that application providers could also qualify. It emphasized clear information about processing purposes and sharing, privacy-friendly defaults, and the rights of people who were not network members. (WP29 Opinion 5/2009, sections 3.1–3.3, 3.5, 3.9.)
Those concerns help explain the setting for Fashion ID, especially its attention to people whose data reach a social network without their having joined it. The Opinion provides historical context under the Directive. The later EDPB guidelines explain how the joint-controllership principles apply under the GDPR.
EDPB guidance explains joint participation
The EDPB’s Guidelines 07/2020 on controllers and processors expressly use Fashion ID. Joint participation may result from common decisions or converging decisions that complement one another and are necessary for the processing. Closely linked purposes can support joint control, but mutual commercial benefit alone is insufficient. Both purposes and means must be examined. (Guidelines 07/2020, paras. 51–55, 59–68.)
- Under Article 26 GDPR, joint controllers must allocate their compliance responsibilities transparently and make the essence of their arrangement available to individuals. The allocation must reflect actual roles; it does not prevent individuals from exercising rights against each joint controller. (Guidelines 07/2020, Part II, section 2.)
Practice Tip: Record the jointly controlled operations and allocate the associated compliance tasks. A contract’s role labels should reflect what the parties actually decide and do.
Targeting can involve a wider set of jointly controlled operations
Guidelines 8/2020 on targeting social media users provide a more recent analysis of the responsibilities of social media providers and organizations using their targeting tools. They expressly build on Fashion ID, while focusing on targeting registered users rather than comprehensively addressing non-members. (Guidelines 8/2020, sections 2, 4.5.)
- Their pixel-based targeting example identifies joint control over collection and transmission, matching, advertisement display, and campaign reporting. The parties’ participation in that campaign supports a broader scope than the collection-and-transmission stage identified in Fashion ID. The guidance also addresses prior consent for tracking technologies and subsequent processing. (Guidelines 8/2020, sections 5.3.1–5.3.2.)
- The practical implication is that Fashion ID’s boundary must be applied to the decisions made in the particular arrangement. Transmission is not a universal endpoint for joint control.
What the Court did—and did not—decide
The Court held that a website operator can jointly control the collection and transmission enabled by an embedded social plugin, even without access to the data. It tied that status, and the associated consent and information duties, to the operations the operator actually helps determine.
It did not make Fashion ID responsible as a controller for all of Facebook’s subsequent processing. Nor did it establish that every embedded feature, shared infrastructure, or commercial relationship creates joint controllership.
It did not decide that commercial interests justified the disputed processing under Article 7(f). It identified whose interests must be considered and reiterated the cumulative requirements of that provision.
It also left the relevant ePrivacy factual question to the national court and did not answer the alternative question about national liability for a non-controller, given its answer on controllership. (Judgment, paras. 74–86, 90–97.)
Conclusion
Fashion ID makes the decision to embed a tool legally significant when that decision enables personal-data processing for purposes the operator shares or helps determine.
The resulting responsibility has a defined scope. Organizations should identify the collection and transmission they enable, examine whether they participate in later processing, and ensure that the relevant information and consent reach individuals at the right time. The absence of data on the organization’s own servers does not answer those questions.
Sources and Useful Reading
Sources
CJEU judgments, Advocate General opinions, and related case materials are available through InfoCuria, the Court of Justice of the European Union’s official case-law database. The case can be located using Case C-40/17, Fashion ID GmbH & Co. KG v Verbraucherzentrale NRW eV.
- Court of Justice of the European Union, Second Chamber, Case C-40/17, Fashion ID GmbH & Co. KG v Verbraucherzentrale NRW eV, Judgment of 29 July 2019, ECLI:EU:C:2019:629. Read the Judgment.
- Opinion of Advocate General Michal Bobek, Case C-40/17, delivered 19 December 2018, ECLI:EU:C:2018:1039. Read the Opinion.
- European Data Protection Board, Guidelines 07/2020 on the concepts of controller and processor in the GDPR, Version 2.1. Explains joint participation in determining purposes and means, including through complementary decisions, and the allocation of responsibilities under Article 26 GDPR. The guidance expressly incorporates Fashion ID. Read the Guidelines.
- European Data Protection Board, Guidelines 8/2020 on the targeting of social media users. Applies Fashion ID to social media targeting, including pixel-based collection, transmission, matching, advertising, and reporting. Particularly useful for understanding when joint control extends beyond the initial transfer. Read the Guidelines.
Useful reading from The de la Torre Review
- Google Spain: The “Right to Be Forgotten”—While the Past Remains Online — Explains why search-engine processing creates controller responsibilities separate from those of the original publisher, even when the underlying information remains lawfully online. That distinction helps frame Fashion ID: responsibility depends on the particular processing an organization determines, rather than simply where the information originates or who possesses it. Read the Article.
- Rijkeboer: When the Right of Access Reaches Into the Past — Explores how access to past disclosure records makes data-protection rights effective. Fashion ID cites Rijkeboer to establish that controllers must inform individuals when their personal data are collected, connecting transparency at collection with accountability afterward. (Fashion ID, para. 104, citing Rijkeboer, para. 68.) Read the Article.
- Jehovan: When Door-to-Door Notes Create Joint Control — Explains why an organization can be a joint controller without accessing the personal data or issuing written collection instructions. It provides an important foundation for Fashion ID’s conclusion that joint control depends on participation in determining the purposes and means of the relevant processing, rather than possession of the data. Read the Article.
- Wirtschaftsakademie: When a Facebook Page Creates Joint Control — Explains the foundation for Fashion ID’s approach to joint control: a page administrator can participate in determining processing through audience and statistical parameters, even when it receives only anonymous reports. The judgment establishes that access to personal data is unnecessary and that joint responsibility need not be equal. Read the Article.
- What Is a Controller? — Explains the functional test underlying Fashion ID: controller status depends on an organization’s actual influence over the purposes and means of processing, rather than its title or contractual designation. Provides the foundation for understanding why embedding a third-party tool can create controller responsibilities. Read the Article.
- What Are ‘Joint Controllers’ (a.k.a. ‘Co-Controllers’)? — Examines how organizations jointly determine processing, why their participation need not be equal, and how they allocate responsibilities under Article 26 GDPR. Provides the broader framework for Fashion ID’s distinction between jointly controlled operations and processing outside an organization’s influence. Read the Article.
- What Are “Legitimate Interests” Under the GDPR? — Explains the three-part Legitimate Interests Assessment: identifying a legitimate interest, establishing necessity, and balancing that interest against individuals’ rights and freedoms. Provides practical context for Fashion ID’s holding that each joint controller must pursue a legitimate interest, while commercial benefit alone does not establish lawfulness. Read the Article.
- What Is “Consent” Under the GDPR? — Examines the requirements for freely given, specific, informed, and unambiguous consent, together with practical guidance on obtaining and managing it. Complements Fashion ID’s analysis of who must obtain consent and why it must precede the collection and transmission it authorizes. Read the Article.
- EU Data Protection Law and the General Data Protection Regulation (GDPR) — Provides a broader introduction to Europe’s data-protection framework, including its key principles, individual rights, lawful bases, and compliance obligations. Places Fashion ID within a framework that regulates how personal data are processed, regardless of whether the information is private or publicly available. Read the Guide. Access requires a free membership.
Comments ()