BE: When GDPR Complaints and Court Proceedings Run in Parallel
Can a GDPR complaint and a lawsuit proceed at the same time? In BE, the CJEU confirmed that administrative and judicial remedies are concurrent and independent, while requiring national rules to preserve effective protection and address the risk of conflicting decisions.
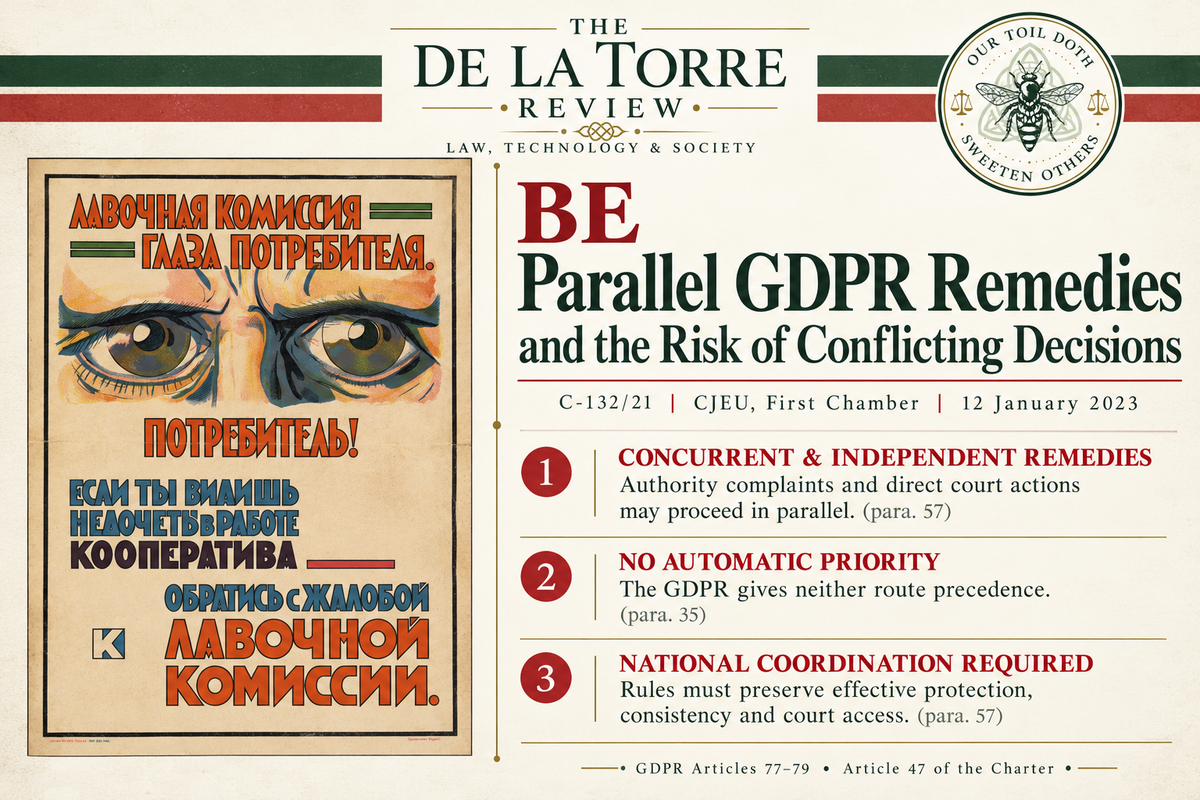
Case C-132/21 | BE v Nemzeti Adatvédelmi és Információszabadság Hatóság | Court of Justice of the European Union | First Chamber | 12 January 2023
Practice Takeaways: ① Administrative and judicial remedies may proceed concurrently and independently. A supervisory-authority complaint and direct proceedings against a controller or processor can concern the same alleged infringement. ② Neither route has automatic priority under the GDPR. ③ Member States must regulate their relationship while preserving effective protection and access to a court. ④ Conflicting judicial decisions can weaken protection by creating legal uncertainty and undermining consistent application of the GDPR.
An individual who believes that their GDPR rights have been infringed can complain to a supervisory authority and bring proceedings against the controller. But what happens when those routes produce different answers about the same processing?
In BE v Nemzeti Adatvédelmi és Információszabadság Hatóság, C-132/21, the Court of Justice held that the GDPR permits those remedies to be exercised concurrently and independently. The Regulation does not give either route automatic priority. Member States must establish procedural rules governing their relationship while preserving effective protection, consistent application of the GDPR, and access to a court.
The case illustrates a distinction between having independent remedies and allowing contradictory decisions to undermine the protection those remedies provide.
What happened
BE attended a company’s general meeting as a shareholder and asked questions of its directors and other participants. He subsequently requested the sound recording of the meeting.
The company provided excerpts reproducing BE’s own contributions but excluded the contributions of other participants, including the answers to his questions. BE complained to the Hungarian supervisory authority, asking it to find that the company had infringed the GDPR and to order disclosure of the recording. The authority rejected his request. (Judgment, paras. 11–13.)
BE pursued two routes:
- Judicial review of the supervisory authority’s decision, under Article 78(1).
- Direct proceedings against the controller, under Article 79(1), initiated alongside his complaint to the authority.
The direct proceedings resulted in a final judgment finding that the controller had infringed BE’s right of access. The challenge to the supervisory authority’s decision remained pending. (Judgment, paras. 14–16.)
The court reviewing the authority’s decision therefore faced the same facts and alleged infringement that a civil court had already considered. It asked whether one route took priority and how the risk of contradictory decisions should be addressed. (Judgment, paras. 17–22.)
Why the case matters
The GDPR provides several avenues for enforcing data protection rights.
| Provision | Remedy | What it addresses |
|---|---|---|
| Article 77(1) | Complaint to a supervisory authority | Processing that the data subject considers infringes the GDPR |
| Article 78(1) | Judicial remedy against a legally binding supervisory authority decision | The lawfulness of the authority’s decision concerning the person bringing the challenge |
| Article 79(1) | Judicial remedy against a controller or processor | An alleged infringement of the data subject’s GDPR rights resulting from processing |
BE confirms that a supervisory-authority complaint and direct judicial proceedings against a controller may concern the same processing while remaining independently available. Each remedy preserves the others through its “without prejudice” language, and neither route automatically takes priority. (Judgment, paras. 33–35.)
That choice strengthens protection but creates a practical challenge: different proceedings can produce conflicting answers about whether the same conduct infringed the GDPR. Procedural rules therefore form part of effective data protection. Member States must regulate how the remedies interact while preserving meaningful court access and addressing legal uncertainty that could weaken the rights being enforced. (Judgment, paras. 45–57.)
For organizations, a favorable supervisory-authority decision does not, by itself, resolve related court proceedings. For individuals, the availability of parallel remedies must be considered alongside the national rules governing their interaction. The practical value of multiple remedies depends on their ability to deliver effective and consistent protection.
Independent remedies must work together to provide effective protection.
Key holding
The Court reached three principal conclusions:
- The GDPR’s administrative and judicial remedies may be exercised concurrently and independently. The supervisory-authority route under Articles 77(1) and 78(1) can proceed alongside direct judicial proceedings against a controller or processor under Article 79(1). (Judgment, para. 57.)
- Neither route has automatic priority under the GDPR. The Regulation establishes no exclusive competence or rule of precedence governing the authority’s and courts’ assessments of whether an infringement occurred. (Judgment, para. 35.)
- Member States must establish rules governing the relationship between the remedies. Those rules must preserve effective protection of GDPR rights, consistent and homogeneous application of the Regulation, and the right to an effective judicial remedy under Article 47 of the Charter. (Judgment, para. 57.)
The Court’s analysis
1. The remedies can be exercised concurrently and independently
The Court began with the wording of Articles 77 to 79. Those provisions make different remedies available without making one dependent on the other.
- The GDPR establishes no priority, exclusive competence, or rule of precedence governing the authority’s and courts’ assessments of whether an infringement occurred. Judicial review of a supervisory authority’s decision and direct proceedings against the controller may therefore proceed concurrently and independently. (Judgment, paras. 33–35.)
- The Court connected this choice to the GDPR’s protective purpose. Making several remedies available strengthens data subjects’ rights and supports the right to an effective judicial remedy under Article 47 of the Charter. (Judgment, paras. 42–44.)
The GDPR does not establish a compulsory sequence in which the supervisory authority must decide an infringement before a court can consider it.
2. The GDPR does not supply a complete coordination mechanism for proceedings within one Member State
The Court distinguished the dispute from situations involving authorities or courts in different Member States.
- Articles 60 to 63 provide cooperation and consistency mechanisms for supervisory authorities. Article 81 addresses related proceedings before courts in different Member States, including possibilities for suspension and, in specified circumstances, declining jurisdiction. (Judgment, paras. 37–39.)
- The GDPR does not provide equivalent rules for coordinating a supervisory authority complaint and judicial proceedings brought within the same Member State concerning the same processing. (Judgment, para. 40.)
That gap matters: the existence of independent remedies does not itself explain how national institutions should manage overlapping proceedings or the effects of an earlier judgment.
3. Judicial review of the supervisory authority must encompass relevant facts and law
Under Article 78(1), read in light of recital 143, a court reviewing a supervisory authority’s decision must exercise full jurisdiction. That includes examining all questions of fact and law relevant to the dispute. (Judgment, para. 41.)
The supervisory authority’s role in enforcing the GDPR therefore does not give its assessment automatic precedence over judicial scrutiny.
At the same time, the Court did not prescribe a universal rule making a judgment in the direct proceedings automatically binding in the judicial review proceedings. It addressed the relationship between the remedies through national procedural autonomy, subject to EU law safeguards.
4. Member States must establish rules governing the relationship between the remedies
In the absence of EU rules governing the issue, Member States must lay down the detailed administrative and judicial procedures needed to protect rights derived from EU law. The referring court must determine how the remedies operate under the applicable national procedural rules. (Judgment, paras. 45–46.)
That discretion has limits:
- Equivalence: The rules must not be less favourable than those governing similar domestic actions.
- Effectiveness: They must not make exercising EU rights practically impossible or excessively difficult.
- Effective judicial protection: They must respect Article 47 of the Charter, including the rights to an effective remedy and a fair trial.
The practical arrangements must not disproportionately restrict access to a court. (Judgment, paras. 47–51.)
5. Contradictory judicial decisions would weaken GDPR protection
The Hungarian court explained that, under national law, it was not bound by the judgment in the direct proceedings, even though both cases concerned the same facts. That created a possibility of contradictory judicial decisions. (Judgment, paras. 52–53.)
The Court identified two problems with that outcome.
- First, opposing decisions about the same infringement would call into question the GDPR’s objective of consistent and homogeneous application.
- Second, the resulting legal uncertainty would weaken the protection of individuals. (Judgment, paras. 54–56.)
The operative ruling therefore combines two requirements: the remedies must remain concurrently and independently available, and national rules must govern their relationship in a way that protects GDPR rights, consistency, and effective judicial protection. (Judgment, para. 57.)
The Advocate General’s Opinion
Advocate General Richard de la Tour also concluded that the GDPR permits parallel remedies and gives neither route priority. He explained that supervisory authorities’ responsibility for overseeing GDPR compliance does not confer priority competence over courts to determine whether an infringement occurred. (Opinion, points 43–50.)
- His proposed answer addressed the effect of the civil judgment more directly. He considered that the court reviewing the supervisory authority’s decision should not be bound by the finding of the court hearing the direct action, because it must remain able to review the authority’s decision fully and independently. (Opinion, points 51–54, 71.)
- He also emphasised that Member States must establish procedural mechanisms to address the risk of contradictory decisions. As illustrations, he discussed exhaustion of administrative remedies and stays of proceedings. (Opinion, points 57–70.)
Those illustrations were proposals in the Opinion. The Court’s judgment did not expressly approve either mechanism. Its ruling instead states the requirements that national coordination rules must satisfy.
What the Court Did—and Did Not—Decide
The Court decided how the GDPR’s enforcement routes relate to one another. It did not resolve the substantive scope of BE’s access request.
The national civil court’s finding that the controller had infringed the right of access formed part of the background. The CJEU did not itself decide whether Article 15 required disclosure of the other participants’ recorded contributions or the entire meeting recording. (Judgment, paras. 11–17, 30, 57.)
Nor did the judgment establish a uniform EU rule governing the binding effect of every judgment delivered in parallel GDPR proceedings. It left detailed coordination to national procedural law, within the limits imposed by EU law.
Conclusion
BE makes coordination a practical priority whenever a complaint, judicial review, and direct action concern the same processing. Parties should identify related proceedings early, maintain consistent factual records, and distinguish the supervisory authority’s decision from the court’s review of that decision.
The applicable national procedural rules remain essential because the GDPR does not fully regulate overlapping proceedings within one Member State. Those rules must preserve equivalence, effectiveness, and the right to an effective judicial remedy.
Sources
Sources and Useful Reading
CJEU judgments, Advocate General opinions, and related case materials are available through InfoCuria, the Court of Justice of the European Union’s official case-law database. The case can be located using Case C-132/21, BE v Nemzeti Adatvédelmi és Információszabadság Hatóság, also indexed under Budapesti Elektromos Művek.
- Court of Justice of the European Union, First Chamber, Case C-132/21, BE v Nemzeti Adatvédelmi és Információszabadság Hatóság, Judgment of 12 January 2023, ECLI:EU:C:2023:2.
- Opinion of Advocate General Richard de la Tour, Case C-132/21, delivered 8 September 2022.
Useful reading from The de la Torre Review
- Puškár: Tax Fraud Lists, Court Access, and the Limits of Procedural Barriers — Explains why national procedural requirements must preserve effective judicial protection and must not disproportionately restrict access to a court. BE cites Puškár when applying those principles to the relationship between the GDPR’s parallel remedies. (BE, Judgment, paras. 49–51.) Read the Article.
- Facebook Ireland and Others: The Limits of the GDPR’s One-Stop Shop — Cited in BE for the requirement that competent national authorities ensure a high level of protection of the rights guaranteed by Article 16 TFEU and Article 8 of the Charter. Supports the Court’s explanation of why concurrent remedies strengthen GDPR protection. (BE, para. 43, citing Facebook Ireland and Others, para. 45.) Read the Article.
Comments ()