Probst: Selling a Debt Does Not Remove Control Over Communications Data
In Probst, the CJEU allowed a telecommunications provider to transfer traffic data to a debt purchaser for collection, provided the purchaser processed only necessary data and acted exclusively under the provider’s instructions and control.
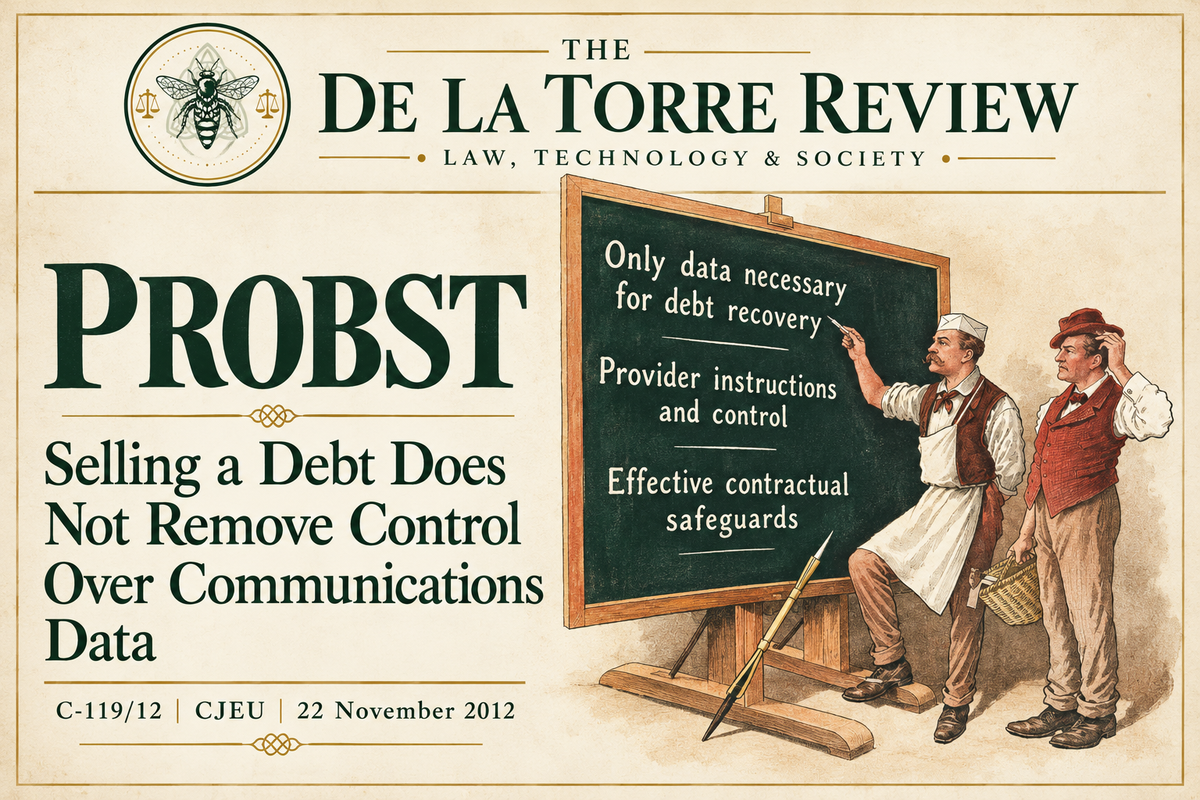
Case C-119/12 | Josef Probst v mr.nexnet GmbH | Court of Justice of the European Union | Third Chamber | 22 November 2012
Practice Takeaways: ① Assigning a telecommunications debt does not give the purchaser unrestricted use of the associated traffic data. ② Processing must remain under the provider’s instructions and control. ③ Only data necessary for collection may be processed. ④ Contracts must enable the provider to ensure continuing compliance.
Can a telecommunications provider sell an unpaid debt and give the purchaser the communications data needed to collect it? If the purchaser owns the debt and bears the risk of nonpayment, must it still follow the provider’s instructions when processing those data?
In Probst, the Court distinguished ownership of a payment claim from authority over the associated traffic data. The transfer could be permitted, but the provider had to retain control over the processing.
NOTE: The judgment interpreted Article 6(2) and (5) of Directive 2002/58, the ePrivacy Directive, in the context of Directive 95/46. It was not a judgment applying the GDPR.
What happened
Josef Probst used internet access services supplied by Verizon through his Deutsche Telekom telephone line. When he failed to pay the charges, nexnet sought payment as the purchaser of the debt under a factoring agreement. Nexnet bore the risk of debtor default. (Judgment, para. 11.)
The contractual arrangements included a data protection and confidentiality agreement restricting data use and providing for oversight, deletion, and return. Probst challenged the assignment’s validity, arguing that it violated German telecommunications law. The dispute reached the Bundesgerichtshof, Germany’s Federal Court of Justice. (Judgment, paras. 12–14.)
That court asked whether the ePrivacy Directive allowed the transfer under the contractual conditions described. Its concern was whether general confidentiality commitments were sufficient or whether the provider needed continuing authority over the purchaser’s use of the data. (Judgment, paras. 14–15.)
Why the case matters
robst distinguishes ownership of a debt from control over the associated traffic-data processing. Purchasing the payment claim did not give the purchaser unrestricted use of those data: processing had to remain necessary for collection and subject to the provider’s instructions and control.
This distinction connects with the GDPR’s functional approach to controller and processor roles, which examines actual decision-making over the particular processing. For more, see What Is a Controller? and What Is a Processor?.
Selling the payment claim does not remove the conditions governing use of the associated traffic data.
The judgment also required enforceable contractual safeguards, including oversight and deletion or return. Today, Article 28 GDPR provides more detailed requirements for controller–processor relationships. See Controller-to-Processor Transfers: What Article 28 GDPR Requires for further guidance.
Key holding
The Court held that Article 6(2) and (5) permitted a provider to transfer traffic data to the assignee of its telecommunications payment claims, and permitted the assignee to process those data, subject to two conditions:
- The assignee must act under the provider’s authority when processing the data.
- Processing must be limited to traffic data necessary to recover the assigned claims.
Acting under the provider’s authority meant acting exclusively on its instructions and under its control. The contract had to guarantee lawful processing and enable the provider to ensure compliance at all times. (Judgment, paras. 29–30.)
The Court’s analysis
1. Billing permitted limited processing of traffic data
The Court read Article 6(2), concerning traffic data needed for billing, together with Article 6(5), which restricted who could process those data and required processing to remain necessary for the permitted activity.
Together, those provisions allowed processing for recovery of assigned payment claims, subject to the authority and necessity requirements. (Judgment, paras. 17–19.)
2. Authority required instructions and control
The Court interpreted acting under another person’s authority as acting on that person’s instructions and under that person’s control. This interpretation reflected both the wording and the protective purpose of the Directive. (Judgment, paras. 20–26.)
The result did not depend on how the assignment contract was classified. Acquiring the debt did not dispense with the provider’s authority over traffic-data processing. (Judgment, para. 27.)
3. Exceptions to confidentiality required strict interpretation
Article 5(1) established confidentiality of communications and related traffic data. Article 6(2) and (5) permitted an exception for billing-related processing.
- Because those provisions departed from confidentiality, they required strict interpretation. The collection purpose could not support processing beyond the exception’s conditions. (Judgment, paras. 22–23.)
4. Outsourcing had to preserve protection
The Court read the ePrivacy provisions alongside Articles 16 and 17 of Directive 95/46 (the Data Protection Directive). Those provisions required processors to follow the controller’s instructions and required the controller to ensure compliance with agreed protective measures. (Judgment, paras. 24–25.)
Article 6(5) allowed providers to use outside companies for activities such as debt collection while preserving the user’s level of data protection. (Judgment, para. 26.)
Practice Tip: Review whether the agreement gives the provider usable powers to direct processing, check compliance, and require deletion or return. A general promise to comply with data protection law does not, by itself, demonstrate continuing control.
5. The contractual safeguards needed to work in practice
The national court had to determine whether the arrangements satisfied these requirements. The CJEU nevertheless indicated that the described contract appeared to do so because it:
- Limited processing to what was necessary for debt recovery.
- Required erasure or return once the data were no longer necessary.
- Allowed the provider to check compliance with security and data protection requirements.
- Allowed the provider to require erasure or return on request.
These provisions supported the continuing control required by the Directive. (Judgment, paras. 27–28.) For the corresponding contractual requirements under the GDPR, see Controller-to-Processor Transfers: What Article 28 GDPR Requires.
The Advocate General’s Opinion
No Advocate General’s Opinion was delivered. Advocate General Pedro Cruz Villalón was assigned to the case, but the Court decided, after hearing him, to proceed to judgment without an Opinion.
What the Court did—and did not—decide
The Court established the conditions under which the transfer and processing could be permitted. It left the national court to determine whether those conditions were met in the particular arrangements. (Judgment, para. 28.)
The judgment did not give debt purchasers a general entitlement to use communications data for their own purposes. Its answer concerned traffic data necessary to recover assigned telecommunications payment claims.
Nor should it be treated as a universal classification of debt collectors under the GDPR. The ruling addressed the specific requirement in the ePrivacy Directive that the relevant processing remain under the provider’s authority.
Conclusion
Probst permitted the transfer of necessary traffic data for debt recovery while requiring the telecommunications provider to retain effective authority over their processing.
The practical lesson is to assess the data arrangements separately from the debt transaction: permitted uses, instructions, oversight, and deletion or return must remain enforceable throughout collection.
Sources and Useful Reading
Sources
CJEU judgments, Advocate General opinions, and related case materials are available through InfoCuria, the Court of Justice of the European Union’s official case-law database. This case can be located using Case C-119/12, Probst.
- Court of Justice of the European Union, Third Chamber, Case C-119/12, Josef Probst v mr.nexnet GmbH, Judgment of 22 November 2012, ECLI:EU:C:2012:748.
Directive 2002/58/EC (ePrivacy Directive), particularly Articles 5 and 6.
Directive 95/46/EC (Data Protection Directive), particularly Articles 16 and 17, concerning instructions and security of processing. Read the Directive.
Useful reading from The de la Torre Review
- Promusicae: When an IP Address Becomes a Person — Examines communications confidentiality and disclosure of personal data for civil enforcement. Probst cites Promusicae, paragraph 48, when explaining the billing exception to confidentiality. (Probst Judgment, para. 23.) Read the Article.
- Tele2 Sverige and Watson and Others: When Fighting Crime Cannot Justify Retaining Everyone’s Communications Data — Applies strict interpretation to national restrictions on communications confidentiality. Tele2 cites Probst, paragraph 23, by analogy when explaining the limits of Article 15(1). (Tele2 Judgment, para. 89.) Read the Article.
- What Is a Controller? — Explains how determining the purposes and means of processing establishes controller status. Provides context for Probst’s distinction between ownership of a debt and control over the associated traffic-data processing. Read the Article.
- What Is a Processor? — Explains processing on a controller’s behalf, the importance of instructions, and the limits of processor discretion. Complements Probst’s analysis of acting under the provider’s authority and control. Read the Article.
- Controller-to-Processor Transfers: What Article 28 GDPR Requires — Explains the GDPR’s requirements for processor contracts, including instructions, security, audits, and deletion or return. Provides the current contractual framework alongside Probst’s earlier analysis under the ePrivacy and Data Protection Directives. Read the Article.
Comments ()