La Quadrature du Net: When National Security Can Justify Retaining Everyone’s Communications Data
In La Quadrature du Net, the CJEU held that a serious national-security threat can justify temporary general retention of traffic and location data under strict safeguards. Fighting serious crime alone cannot justify the same measure.
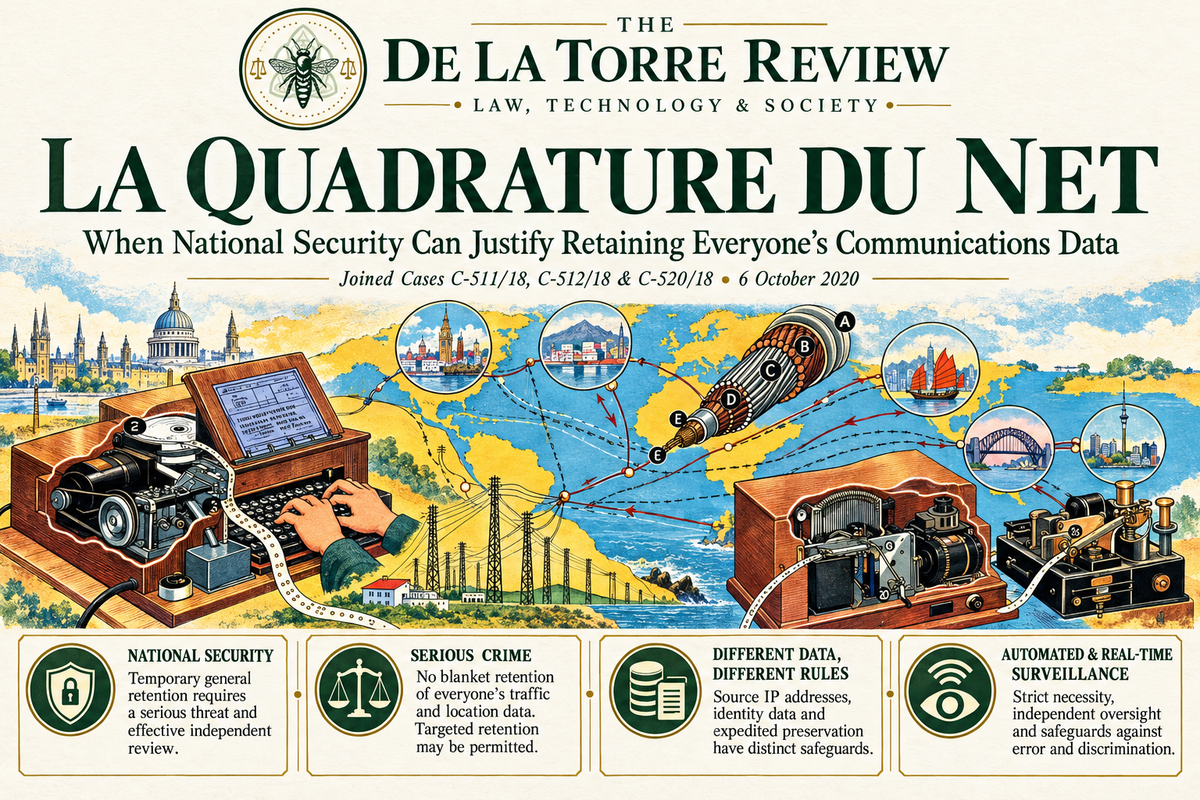
Joined Cases C-511/18, C-512/18 and C-520/18 | La Quadrature du Net and Others v Premier ministre and Others; Ordre des barreaux francophones et germanophone and Others v Conseil des ministres | Court of Justice of the European Union | Grand Chamber | 6 October 2020
Practice Takeaways: ① National-security legislation requiring communications providers to process data remains subject to the ePrivacy Directive. ② A serious national-security threat shown to be genuine and present or foreseeable can justify temporary general retention of traffic and location data, with effective independent review. ③ Targeted retention, source IP addresses, civil-identity data, and expedited preservation require distinct assessments. ④ Automated screening and real-time collection have their own limits, including safeguards against discrimination and erroneous results. ⑤ Unlawful retention cannot simply continue while national law is repaired, and its consequences for criminal evidence require a separate assessment.
Can a government require providers to retain everyone’s communications data to protect national security? Does the answer change when the objective is investigating crime, identifying an Internet user, or detecting a terrorist threat through automated analysis?
In La Quadrature du Net and Others, the Court developed a detailed framework for answering those questions. It maintained Tele2’s prohibition on general and indiscriminate retention of traffic and location data for fighting serious crime. It also recognized a narrowly conditioned national-security exception and distinguished several other forms of retention and surveillance.
NOTE: This article examines the judgment of 6 October 2020 in Joined Cases C-511/18, C-512/18 and C-520/18. Its principal framework is Article 15(1) of the ePrivacy Directive, interpreted in light of the Charter. The judgment also addresses Article 23 GDPR. The discussion describes this ruling’s holdings rather than presenting a consolidated account of subsequent surveillance case law.
Practice Tip: Identify the data, the processing operation, and the public-interest objective before assessing a retention requirement. A rule governing subscriber identity cannot automatically be applied to communications histories or continuous location tracking.
What happened
The judgment brought together three references concerning French and Belgian legislation.
- In Case C-511/18, La Quadrature du Net and other organizations challenged French decrees implementing intelligence-gathering powers. The proceedings concerned providers’ retention of connection data, automated analysis designed to detect terrorist threats, and real-time collection of traffic and location data. The French Conseil d’État asked whether the national-security context and existing safeguards could justify these measures. It also questioned whether affected people had to be notified once notification would no longer jeopardize the authorities’ work. (Judgment, paras. 56–68.)
- Case C-512/18 concerned a challenge to the French Prime Minister’s failure to repeal rules requiring the general retention of communications data and information capable of identifying people who contributed to online content. The reference raised the relationship between the ePrivacy Directive and the e-Commerce Directive, as well as the permissibility of broad retention obligations. (Judgment, paras. 69–72.)
- In Case C-520/18, professional bodies, civil-society organizations, and individuals challenged Belgium’s Law of 29 May 2016 on the collection and retention of electronic communications data. The Belgian Constitutional Court asked about retention for national security, criminal investigations, and other public purposes, including the protection of children. It also asked whether the effects of incompatible legislation could temporarily be maintained. (Judgment, paras. 73–79.)
The cases required the Court to consider both the reach of EU law and the distinctions necessary to apply strict necessity to different surveillance measures.
Why the case matters
Digital Rights Ireland invalidated the EU Data Retention Directive. Tele2 then applied the ePrivacy Directive and the Charter to national retention laws. La Quadrature du Net addressed national security expressly and explained why the answer depends on the particular measure under review. (Judgment, paras. 134–168.)
The Court distinguished a population-wide communications history from a database identifying subscribers. It also distinguished preserving existing records from collecting information continuously in real time. Those differences determine the seriousness of the interference and the objectives capable of justifying it.
The justification must match what the data and the surveillance technique can reveal.
The judgment also rejected the proposition that invoking national security automatically removes obligations imposed on private providers from EU law. Member States retain responsibility for national security, but measures regulating providers’ processing remain subject to the applicable EU framework. (Judgment, paras. 95–104.)
Key holding
The Court reached four principal conclusions:
- General retention remained prohibited as a preventive default, subject to specifically defined permissible measures. A serious national-security threat could justify a temporary instruction requiring general retention of traffic and location data, with effective review. The Court also permitted, under distinct conditions, targeted retention, general retention of source IP addresses, general retention of civil-identity data, and expedited preservation of existing records. Clear and precise rules and effective safeguards were required. (Judgment, para. 168.)
- Automated analysis and real-time collection required separate safeguards. Population-wide automated analysis could be justified by a serious national-security threat shown to be genuine and present or foreseeable, subject to effective review. Real-time collection required a valid reason to suspect involvement in terrorist activities and, generally, prior independent review. (Judgment, paras. 177–192.)
- The e-Commerce Directive did not govern the data-protection question. Retention obligations imposed on online-access and hosting providers had to be assessed under the ePrivacy Directive or the GDPR, as appropriate. Article 23 GDPR did not permit the general and indiscriminate retention obligation at issue. (Judgment, paras. 197–212.)
- National courts could not temporarily preserve incompatible retention legislation through national rules limiting the effects of a declaration of illegality. Criminal-evidence rules remained principally a matter for national law, subject to equivalence and effectiveness, including a duty to disregard evidence in the particular circumstances identified by the Court. (Judgment, paras. 213–228.)
The Court’s analysis
1. National security did not remove providers’ obligations from EU law
Several governments argued that measures protecting national security fell outside the ePrivacy Directive. They relied on Article 4(2) TEU, which reserves national security to the Member States, and Article 1(3) of the Directive, which excludes certain State activities. (Judgment, paras. 89–90.)
- The Court distinguished those State activities from legislation requiring communications providers to process data. Article 15(1) expressly permits restrictions for national security and other specified objectives, subject to conditions. Excluding every measure pursuing those objectives would deprive that provision of practical effect. (Judgment, paras. 91–99.)
Accordingly, obligations requiring providers to retain data or grant authorities access fell within the Directive. Direct State measures that imposed no processing obligations on providers raised a different scope question, which the Court addressed separately. (Judgment, paras. 100–104.)
2. Confidentiality and strict necessity remained the starting point
The Directive establishes confidentiality of communications and related data. Article 15(1) permits legislative exceptions for specified purposes, but those exceptions cannot make systematic retention the ordinary rule. (Judgment, paras. 106–113.)
- Traffic and location data can reveal habits, movements, relationships, and sensitive characteristics. Their combination may produce a profile as sensitive as communications content. Retention itself creates an interference and a risk of abuse, while knowledge of surveillance can deter expression, including communications involving professional secrecy and whistleblowers. (Judgment, paras. 113–119.)
- The Court also recognized States’ positive obligations to protect individuals, particularly children and other vulnerable people. Those obligations had to be reconciled with privacy, data protection, and the safeguards governing investigations. They did not establish an unrestricted power to retain everyone’s communications history. (Judgment, paras. 122–132, 145.)
3. A serious national-security threat could justify temporary general retention
The Court treated national security as protecting the State’s essential functions and society’s fundamental interests against activities capable of seriously destabilizing them, including terrorism. That objective could justify more serious interference than fighting crime or protecting public security. (Judgment, paras. 134–136.)
- General and indiscriminate retention of traffic and location data could therefore be required where sufficiently solid grounds showed a serious threat to national security that was genuine and present or foreseeable. The threat supplied the connection between the population-wide measure and its objective. (Judgment, para. 137.)
The exception nevertheless required meaningful limits:
- The instruction had to last only as long as strictly necessary, with each instruction confined to a foreseeable period.
- Renewal was possible if the threat persisted; retention could not become systematic.
A court or independent administrative body with binding decision-making power had to provide effective review of the threat and the required conditions and safeguards.
(Judgment, paras. 138–139, 168.)
Practice Tip: A national-security label does not establish the factual conditions for general retention. Examine the demonstrated threat, the instruction’s duration, the basis for renewal, and the reviewer’s binding powers.
4. Serious crime could justify targeted retention
The Court reaffirmed that fighting serious crime could not justify general and indiscriminate retention of traffic and location data. Even the importance of preventing serious threats to public security did not make systematic population-wide retention strictly necessary. (Judgment, paras. 140–145.)
- Targeted retention remained possible for national security, fighting serious crime, and preventing serious threats to public security. It had to be limited as to the data, communications, people, and period covered. (Judgment, paras. 146–147.)
- Targeting could rely on objective evidence concerning categories of people, including people previously identified as posing a security threat. It could also use objective and non-discriminatory geographical criteria. The Court mentioned areas with a high incidence of serious crime, particularly vulnerable infrastructure, and strategic locations such as airports and stations. Duration remained subject to strict necessity. (Judgment, paras. 148–151.)
These examples did not create automatic authority to retain data at every busy location. The geographical criterion had to be justified by the relevant risk.
5. Source IP addresses received a distinct assessment
The Court distinguished IP addresses assigned to the source of an Internet connection from broader traffic data, including destination addresses. Source IP addresses can help identify the person associated with an online communication without themselves identifying that person’s contacts. They can nevertheless support extensive tracking and profiling. (Judgment, paras. 152–153.)
- The Court recognized that an IP address may be the only investigative route to identifying the person responsible for an online offense. It specifically discussed serious offenses involving child sexual abuse material. (Judgment, para. 154.)
- Under this judgment, general retention of source IP addresses could be justified for national security, fighting serious crime, or preventing serious threats to public security. The period had to remain strictly necessary, and use of the data required strict substantive and procedural safeguards, particularly against tracking online activity. (Judgment, paras. 155–156, 168.)
6. Civil-identity data could be retained for broader purposes
Civil-identity data, considered on its own, does not reveal the timing, recipients, frequency, or location of communications. The Court therefore regarded retention of that data as an interference that was not, in principle, serious. (Judgment, para. 157.)
- Retention and access solely to identify users, without associating the data with information about their communications, could be justified by investigating criminal offenses generally. The Court permitted general retention of civil-identity data for crime prevention and public security without requiring the offenses or threats to be serious, even where the legislation imposed no specific time limit. Its operative ruling also included national security. (Judgment, paras. 158–159, 168.)
That holding depended on the limited information involved. Combining identity records with a communications history changes the assessment.
7. Expedited preservation could prevent relevant records from disappearing
The Court also permitted expedited retention, often described as a quick freeze, of traffic and location data already held by providers. Such data may have been retained for ordinary service purposes or under a permissible legislative measure and otherwise be due for erasure or anonymization. (Judgment, paras. 160–163.)
- A competent authority could order preservation for a specified period, subject to effective judicial review, to combat serious crime or protect national security. The data had to be capable of shedding light on the relevant offense or threat, and the duration had to remain strictly necessary. (Judgment, paras. 163–164.)
- Preservation could extend beyond suspects to victims, their social or professional circles, or relevant geographical areas, where objective and non-discriminatory factors supported it. Subsequent access still required its own safeguards. Data retained for serious crime or national security could not simply be accessed to prosecute ordinary crime. (Judgment, paras. 165–167.)
8. Automated screening required independent review and safeguards against error
The French automated-analysis system screened users’ traffic and location data against parameters intended to detect terrorist threats.
- The Court treated that screening as general and indiscriminate processing and a particularly serious interference, independently of any later collection concerning identified individuals. The possibility of later identification also meant the screened information remained personal data. (Judgment, paras. 170–174.)
- Such analysis could be justified only in the presence of a serious national-security threat shown to be genuine and present or foreseeable, for a strictly limited period, with effective judicial or independent administrative review. (Judgment, paras. 175–179.)
- The models and criteria had to be specific, reliable, and non-discriminatory. They could not treat sensitive characteristics, in isolation and irrespective of individual conduct, as indicators of terrorist involvement. Positive results required individual examination by non-automated means before an adverse individual measure could be adopted. Models, criteria, and databases also required regular review for reliability and currency. (Judgment, paras. 180–182.)
Practice Tip: Review what happens after a system produces a match. The judgment requires meaningful individual examination before an adverse measure and regular scrutiny of the criteria and databases that generate the results.
9. Real-time collection required an individual link to terrorism
Continuous collection can reveal communications patterns and allow authorities to track a person’s movements as they occur. The Court considered real-time location tracking particularly intrusive and distinguished it from access to historical records. (Judgment, paras. 183–187.)
- Real-time traffic and location collection could be used only where there was a valid reason to suspect that the person was involved in terrorist activities. Collection required objective and non-discriminatory statutory criteria and prior review by a court or an independent administrative body with binding powers. In duly justified urgency, review had to follow within a short time. (Judgment, paras. 188–189.)
- Authorities had to notify people subjected to real-time collection when, and to the extent that, notification would no longer jeopardize their tasks. For automated analysis, general public information sufficed initially. Individual notice became necessary where a match led the authority to identify someone for deeper analysis, subject to the same protection of ongoing tasks. (Judgment, paras. 190–191.)
10. Online service providers remained subject to data-protection law
The Court rejected the e-Commerce Directive as the framework for assessing the confidentiality and personal-data aspects of the retention obligations. Depending on the service, the applicable rules came from the ePrivacy Directive or the GDPR. (Judgment, paras. 197–206.)
Under the GDPR, processing still had to satisfy Articles 5 and 6, subject to permissible restrictions. Article 23 required respect for the essence of fundamental rights, necessity, proportionality, and the specific statutory safeguards in Article 23(2). It could not authorize the general and indiscriminate retention obligation at issue. (Judgment, paras. 207–212.)
11. Incompatible legislation could not simply remain effective
The Belgian court could not use national law to preserve temporarily the effects of retention legislation incompatible with EU law. Doing so would continue obligations that seriously interfered with fundamental rights. (Judgment, paras. 213–220.)
- The treatment of evidence obtained through unlawful retention was a separate question. National law generally governed admissibility and assessment, subject to equivalence and effectiveness. The judgment did not impose automatic exclusion of every item obtained unlawfully. (Judgment, paras. 221–225.)
- However, national criminal courts had to disregard such information and evidence where defendants could not comment on it effectively, it concerned a field outside the judges’ knowledge, and it was likely to have a preponderant influence on the findings of fact. Those conditions protected the adversarial process and the right to a fair trial. (Judgment, paras. 226–228.)
The Advocate General’s Opinion
Advocate General Manuel Campos Sánchez-Bordona delivered his Opinion on 15 January 2020 in the two French cases, C-511/18 and C-512/18. His analysis repeatedly referred to his separate Opinion in the Belgian case, C-520/18.
- He supported applying the ePrivacy Directive to obligations imposed on providers, distinguished the Directive’s scope from the earlier passenger-name-record litigation, and rejected the general retention regime under review. He considered that the terrorist context did not warrant abandoning Tele2’s limits. Operational effectiveness had to remain compatible with fundamental rights and the rule of law. (Opinion, points 65–75, 111–136.)
- He also supported independent review of access, specific and non-discriminatory criteria for automated processing, and notification once investigations would no longer be jeopardized. A remedy depending on people independently discovering or suspecting surveillance did not adequately protect everyone affected. (Opinion, points 137–153.)
The Court agreed with significant parts of that reasoning but articulated its own national-security exception: a demonstrated serious threat could justify a temporary general-retention instruction with effective review. It also developed a more detailed distinction between general information about automated screening and individual notification after identification for deeper analysis. (Judgment, paras. 134–139, 190–191.)
What the Court did—and did not—decide
The judgment supplied a framework for national retention and surveillance legislation. It did not approve every aspect of the French or Belgian schemes or establish that a permanent national-security rationale makes population-wide retention lawful.
Nor did it set a standard permissible retention period. Duration, targeting, access, and oversight had to be assessed against the particular data and objective. Its treatment of source IP addresses was expressly distinct from its treatment of civil-identity data and full communications histories.
The ruling primarily concerned communications metadata and related identifying information. It did not provide a general authorization to intercept communications content. It also did not determine a third country’s adequacy under the GDPR: its Charter analysis is relevant background, but adequacy requires its own legal assessment.
Finally, the refusal to maintain unlawful legislation did not itself determine the outcome of every prosecution involving retained data. The Court separately identified the principles governing evidence and the circumstances requiring it to be disregarded.
Conclusion
La Quadrature du Net preserved the prohibition on general traffic-and-location-data retention for fighting serious crime while recognizing a strictly conditioned response to serious national-security threats.
Its practical value lies in the distinctions it requires. A lawful regime must justify the particular data collected, the people affected, the duration, and the way authorities use the information. Independent review, safeguards against automated error and discrimination, and effective remedies give those limits practical effect.
Sources and Useful Reading
Sources
CJEU judgments, Advocate General opinions, and related case materials are available through InfoCuria, the Court of Justice of the European Union’s official case-law database. The joined cases can be located using Cases C-511/18, C-512/18 and C-520/18, La Quadrature du Net and Others.
- CJEU, Grand Chamber, La Quadrature du Net and Others, Joined Cases C-511/18, C-512/18 and C-520/18, Judgment of 6 October 2020, ECLI:EU:C:2020:791.
- Opinion of Advocate General Manuel Campos Sánchez-Bordona, Joined Cases C-511/18 and C-512/18, delivered 15 January 2020, ECLI:EU:C:2020:6.
Directive 2002/58/EC, particularly Articles 1, 3, 5, 6, 9, and 15. Read the ePrivacy Directive.
Regulation (EU) 2016/679, particularly Articles 5, 6, and 23. Read the GDPR.
Directive 2000/31/EC, particularly Article 1(5)(b). Read the e-Commerce Directive.
Charter of Fundamental Rights of the European Union, particularly Articles 7, 8, 11, 21, 47, and 52. Read the Charter.
Useful reading from The de la Torre Review
- Tele2 Sverige and Watson and Others: When Fighting Crime Cannot Justify Retaining Everyone’s Communications Data — Explains the prohibition on general retention for fighting serious crime and the separate safeguards governing access. La Quadrature du Net draws on Tele2 throughout and reaffirms that prohibition while addressing national security separately. (Judgment, paras. 96–97, 111, 141–151, 165, 189–190.) Read the Article.
- Digital Rights Ireland: Why Communications Metadata Can Reveal a Life — Examines the invalidation of the EU Data Retention Directive and the sensitivity of communications metadata. La Quadrature du Net cites it on profiling, deterrence, strict necessity, safeguards, and the breadth of general retention. (Judgment, paras. 117–118, 130, 132, 143–144.) Read the Article.
- Ministerio Fiscal: Not All Access to Communications Data Is Equally Intrusive — Explains why the seriousness of an interference affects the objectives that can justify it. La Quadrature du Net relies on that distinction when assessing civil-identity data separately from revealing traffic and location data. (Judgment, paras. 131, 157–158.) Read the Article.
- What Is the Charter of Fundamental Rights of the European Union? — Explains the framework for limiting fundamental rights that underlies the judgment’s analysis of surveillance, proportionality, and effective remedies. Read the Article.
- Satakunnan & Satamedia: Public Data Is Still Personal Data — Explains strict necessity when reconciling data protection with competing interests. La Quadrature du Net cites Satakunnan, paragraph 56, for the requirement to limit derogations to what is strictly necessary. (Judgment, para. 130.) Read the Article.
- Promusicae: When an IP Address Becomes a Person — Examines communications confidentiality and competing fundamental rights. La Quadrature du Net cites Promusicae, paragraph 57, when explaining why the e-Commerce Directive cannot undermine ePrivacy and data-protection requirements. (Judgment, para. 200.) Read the Article.

Comments ()